What Are the Risks of DeFi? Smart Contract, Oracle, and Systemic Risks
The main risks of DeFi include smart contract bugs, oracle manipulation, liquidity risk, economic design risk, governance risk, and the systemic risk that arises across protocols. These risks are not independent of one another, and a single protocol may be exposed to several at once. That is why judging the safety of DeFi cannot come down to whether an audit exists, or to TVL and uptime alone.
Why does DeFi carry so many risks?
DeFi runs by handing part of the rules of traditional finance to smart contracts on a blockchain. Your assets, collateral, borrowing, trading, and liquidations may all be handled directly by code and protocol rules.
That design removes many traditional intermediaries, but it also means this: if the code, the data, the incentives, or the dependencies between protocols go wrong, the risk can pass straight through to user assets.
More importantly, DeFi is highly composable.
One protocol may draw on another protocol's tokens, price data, liquidity, or lending market. When a single component fails, the impact may not stay contained to that component; it can spread along the dependencies between protocols.
So understanding DeFi risk is not only a matter of asking:
"Is there a bug in this protocol?"
You also need to ask:
"Which external components does it depend on?" "If those components fail, will my assets be affected?"
Smart contract risk: when code breaks, assets can be hit directly
Smart contract risk is the most fundamental category of DeFi risk.
A smart contract is essentially a program deployed on a blockchain. When you hand your assets to a protocol to manage, you are really interacting with that code.
If a contract contains a logic flaw, an attacker may exploit an abnormal condition to bypass the intended rules and cause asset losses.
Common issues include:
faulty permission control;
reentrancy bugs;
integer calculation problems;
flawed validation logic;
incorrect price or balance calculations;
unsafe external calls;
risks in upgrade mechanisms or admin privileges.
For example, a lending protocol has to correctly assess a user's collateral value and borrowing capacity. If that calculation logic is flawed, an attacker may be able to borrow more than the normal limit through abnormal operations.
So "the smart contract is already deployed" does not mean "the smart contract is absolutely safe."
Even an audited protocol only shows that a security team reviewed it at a particular time and within a particular scope. It cannot guarantee that no new flaw will appear in the future.
Does an audit make a protocol safe?
No.
An audit is an important reference point for judging a protocol's security posture, but it is not proof of absolute safety.
The reason is simple: smart contract systems are usually complex, and a protocol may consist of multiple contracts. An audit covers a specific code version and a specific scope. After deployment, upgrades, new modules, or new external integrations can change the risk structure.
So instead of only asking whether an audit exists, dig further:
What was audited?
Who performed the audit?
When was it performed?
Does the currently deployed code match the audited version?
Does the protocol have admin or upgrade privileges?
These questions are more informative than simply seeing an "audited" badge.
Oracle risk: smart contracts can also "believe the wrong data"
Many DeFi protocols cannot rely only on data that lives on-chain.
A lending protocol, for instance, needs to know the current price of ETH in order to assess collateral value and liquidation conditions. That is where an oracle comes in, feeding information from off-chain or other data sources into the smart contract.
The oracle itself is not the risk; it is critical infrastructure for DeFi to function.
The real problem is this:
If the data an oracle provides is wrong, delayed, or manipulated, a smart contract may execute correct code on the basis of incorrect information.
That means even a contract with no bugs of its own can suffer serious consequences because of bad data.
What are the main sources of oracle risk?
It comes down to three areas:
Data accuracy.
Is the price the oracle provides genuine and reliable?
Data availability.
When the market swings violently or the network misbehaves, can the oracle still update in time?
Manipulation resistance.
Can an attacker manipulate a market or data source so that the oracle reports an abnormal price?
For example, if a protocol relies directly on a low-liquidity on-chain market as its price source, a large trade may move the market price within a short window. If the protocol then uses that abnormal price for collateral valuation or liquidation, an attack opportunity appears.
So the core question about an oracle is not simply whether price data exists, but whether the data is accurate, timely, and difficult enough to manipulate.
Liquidity risk: assets on the books do not guarantee an orderly exit
Liquidity risk is often overlooked.
Suppose a DeFi pool shows a large amount of assets, but part of that is in assets with very little real market depth. If many users exit at the same time, there may not be enough counterparties to absorb the trades.
The result can be:
a rapid drop in price;
severe slippage on large trades;
users unable to exit at the price they expected;
larger losses during liquidations.
So judging a protocol is not just about how much money is locked up; you also need to consider the real liquidity of those assets.
That is also why a high TVL does not automatically mean safety.
If TVL is mostly made up of low-liquidity assets, or if funds are concentrated in a handful of assets and pools, the headline figure does not fully represent the protocol's ability to withstand stress.
Economic design risk: rules without bugs can still be badly designed
Not every DeFi loss comes from a hack.
Some risk comes from the protocol's own economic model.
A protocol might attract liquidity with generous token rewards. If those rewards keep declining while new capital keeps flowing in, the token price and liquidity may come under pressure.
Or a lending protocol's collateral ratio, liquidation threshold, or interest rate mechanism may be poorly designed, producing a wave of liquidations in extreme markets that pushes prices further.
This kind of risk comes down to this:
The code runs exactly as designed, but the design itself can break down under extreme conditions.
So when you study DeFi, looking for bugs in the code is not enough. You also need to understand:
where the yield comes from;
who pays for that yield;
where the token rewards come from;
how the liquidation mechanism works;
what the protocol does in extreme market conditions.
Impermanent loss is part of DeFi risk too
If you provide assets to certain liquidity pools, you may face impermanent loss when prices move significantly.
Say you provide two assets to a trading pool and one of them rises sharply. The automated market maker mechanism keeps rebalancing the ratio of the two assets in the pool.
When you eventually withdraw from the pool, the asset mix you get back may differ from simply holding those two assets.
So the fee income or token rewards you see from liquidity mining do not translate directly into a final net return.
If you are running strategies such as LP or farming, calculate yield, price changes, and impermanent loss together instead of looking only at the APR or APY on the page.
Governance risk: is the protocol really "decentralized"?
DeFi talks about decentralization constantly, but the actual governance structure can vary enormously from one protocol to the next.
Some protocols have admin privileges that can upgrade contracts, change parameters, or take specific actions; some are governed through a DAO; and some may have a small number of addresses holding a large share of governance power.
That is where governance risk comes from.
Key questions to examine:
Who can modify the protocol?
Who can pause functionality?
Who can upgrade contracts?
Is governance power highly concentrated?
Do emergency privileges exist?
If a single address holds excessive power, then even a protocol with no technical flaws can put assets at risk when a privileged key is stolen or misused.
So "decentralized" should not be taken from project marketing alone; look at the protocol's actual permission structure.
Cross-protocol dependencies create systemic risk
This is the most important layer in understanding DeFi risk.
Modern DeFi is not a set of fully independent projects but a web of interconnected financial components.
For example:
user assets → lending protocol → collateral → price oracle → DEX → stablecoin → other protocols
If any key link in that chain fails, other protocols can be affected.
Suppose an asset is widely used as collateral across multiple lending protocols. If its price suddenly moves abnormally, liquidations may be triggered; a wave of liquidations can add further selling pressure; and as the market price keeps falling, more liquidations may follow.
That is a classic case of risk transmission.
Cross-chain bridges are similar. Bridged assets usually depend on smart contracts, validators, or other trust mechanisms, and once a key link is attacked, the risk can spread further to other protocols that rely on that asset.
So DeFi systemic risk often comes from interdependence rather than from any single bug.
What layers can DeFi risk be divided into?
To make this easier to grasp, DeFi risk can be split into five layers:
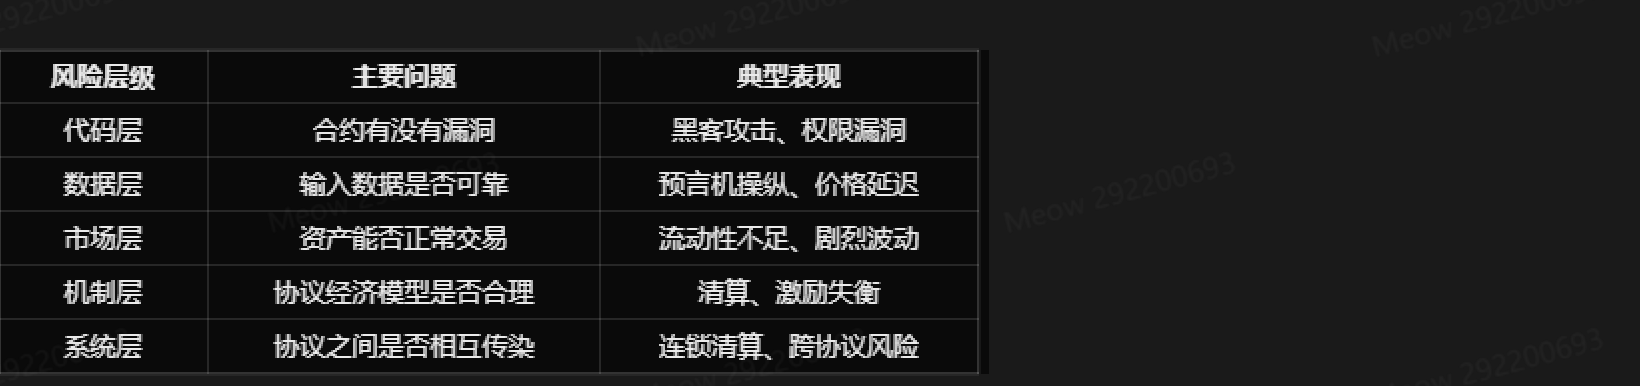
The value of this framework is this: do not examine only one type of risk.
A protocol may have audited smart contracts but a flawed oracle design, or its code may have no obvious bugs while it depends heavily on another high-risk protocol.
So real risk assessment needs to move from "is this one point safe?" to "how does the whole risk chain look?"
How can beginners quickly assess the risk of a DeFi protocol?
If you do not have the technical ability to read every line of a smart contract, start with these six questions.
1. What is the protocol's core function?
First work out what it actually does.
Lending, DEXs, staking, derivatives, and yield aggregators do not share the same risk structure.
2. Where are the assets held?
Confirm which smart contract the assets ultimately enter and whether they pass through other protocols.
The more complex the path, the more dependencies there usually are.
3. Which external components does the protocol depend on?
Focus on:
price oracles;
stablecoins;
cross-chain bridges;
other lending protocols;
DEX liquidity;
third-party yield strategies.
4. Who holds the admin privileges?
Check whether there are:
admin privileges;
contract upgrade privileges;
pause privileges;
parameter change privileges;
multisig control.
5. What happens in extreme market conditions?
This is the question ordinary users overlook most often.
Do not just look at how things run in normal conditions. Also ask:
If the asset price suddenly drops 30% or 50%, can the protocol still liquidate properly?
If many users exit at once, is there enough liquidity?
If the oracle temporarily misbehaves, how does the protocol respond?
6. Is there a single point of dependency?
If a protocol relies heavily on one price source, one stablecoin, one cross-chain bridge, or one external protocol, that corresponding risk deserves extra attention.
How can you reduce the risks of using DeFi?
DeFi risk cannot be eliminated entirely with any single setting, but potential losses can be controlled by reducing your exposure.
Practical approaches include:
Do not put all your assets into a single protocol.
Even a protocol with a long track record does not guarantee that nothing will ever go wrong.
Do not choose a product just because the APY is high.
High yield usually means taking on more risk or facing more complex sources of return.
Verify contracts and what you are interacting with.
Before using a DeFi product, confirm the official website, the contract address, and what you are actually interacting with, so you do not end up on a phishing page.
Limit the scope of approvals.
For operations that require token approvals, make the effort to understand who you are approving and for how much, and avoid unnecessary long-term approval exposure.
Start with a small test.
When using an unfamiliar protocol for the first time, run through the full flow of depositing, trading, and withdrawing with a small amount, and only consider adding more funds once the path works as expected.
If you want to go deeper into specific attack methods such as hacking, flash loans, reentrancy attacks, and oracle manipulation, continue with DeFi Security: Common Attack Methods and How to Defend Against Them, which focuses on how attackers typically profit from protocol flaws or design weaknesses.
The most dangerous thing about DeFi is not one risk but risks stacking up
One way to think about DeFi risk is as a chain:
smart contracts → oracles → liquidity → economic mechanisms → external protocols → systemic risk
If any link in that chain fails, it can affect the others.
For example:
abnormal oracle price → wrong collateral valuation → abnormal borrowing capacity → liquidation mechanism triggered → increased selling pressure → falling collateral value on other protocols → risk keeps spreading
That is why you cannot judge whether a DeFi protocol is safe with simple questions like "has it ever been hacked," "has it been audited," or "how high is its TVL."
What actually deserves attention is this:
what assets does it control, what components does it depend on, who holds the privileges, what happens under extreme conditions, and can the risk be transmitted to other protocols.
FAQ
What is the biggest risk in DeFi?
There is no single "biggest risk." Different protocols face different primary risks, commonly including smart contract bugs, oracle manipulation, liquidity risk, economic design risk, governance risk, and the systemic risk that arises across protocols.
Is a DeFi protocol safe if it has been audited?
No. An audit can help uncover some code and design problems, but it cannot guarantee that a protocol will be absolutely safe in the future. You also need to consider the audit scope, the code version, upgrade mechanisms, and newly added external dependencies.
What is DeFi oracle risk?
Oracles supply smart contracts with off-chain or external data. If price data is wrong, delayed, or manipulated, the lending, liquidation, and other mechanisms that depend on it may execute on incorrect information.
Do DeFi protocols with high TVL carry lower risk?
Not necessarily. TVL mainly reflects the scale of assets in a protocol; it does not directly represent smart contract safety, liquidity quality, governance structure, or systemic risk.
Why does DeFi have systemic risk?
Because protocols depend on each other heavily. A lending protocol, for example, may depend on stablecoins, oracles, and DEX prices. When one key component fails, the problem can spread to other protocols through collateral, liquidations, and liquidity.
How can beginners tell whether a DeFi protocol is safe?
You can quickly check six things: what the protocol does, where assets are held, external dependencies, admin privileges, behavior in extreme markets, and whether any single point of dependency exists. Do not rely only on APY, TVL, or an "audited" label.
Risk Disclaimer
DeFi is a high-risk area of digital asset use. Running a protocol involves multiple risks, including smart contracts, oracles, market liquidity, governance, cross-protocol dependencies, and digital asset price volatility. Even a protocol that has been audited, has operated for a long time, or holds a high TVL does not thereby guarantee asset safety. Before using any DeFi product, make sure you understand the protocol mechanics, the path your funds take, and the potential risks, and make decisions prudently based on your own risk tolerance.
Recommended
View more